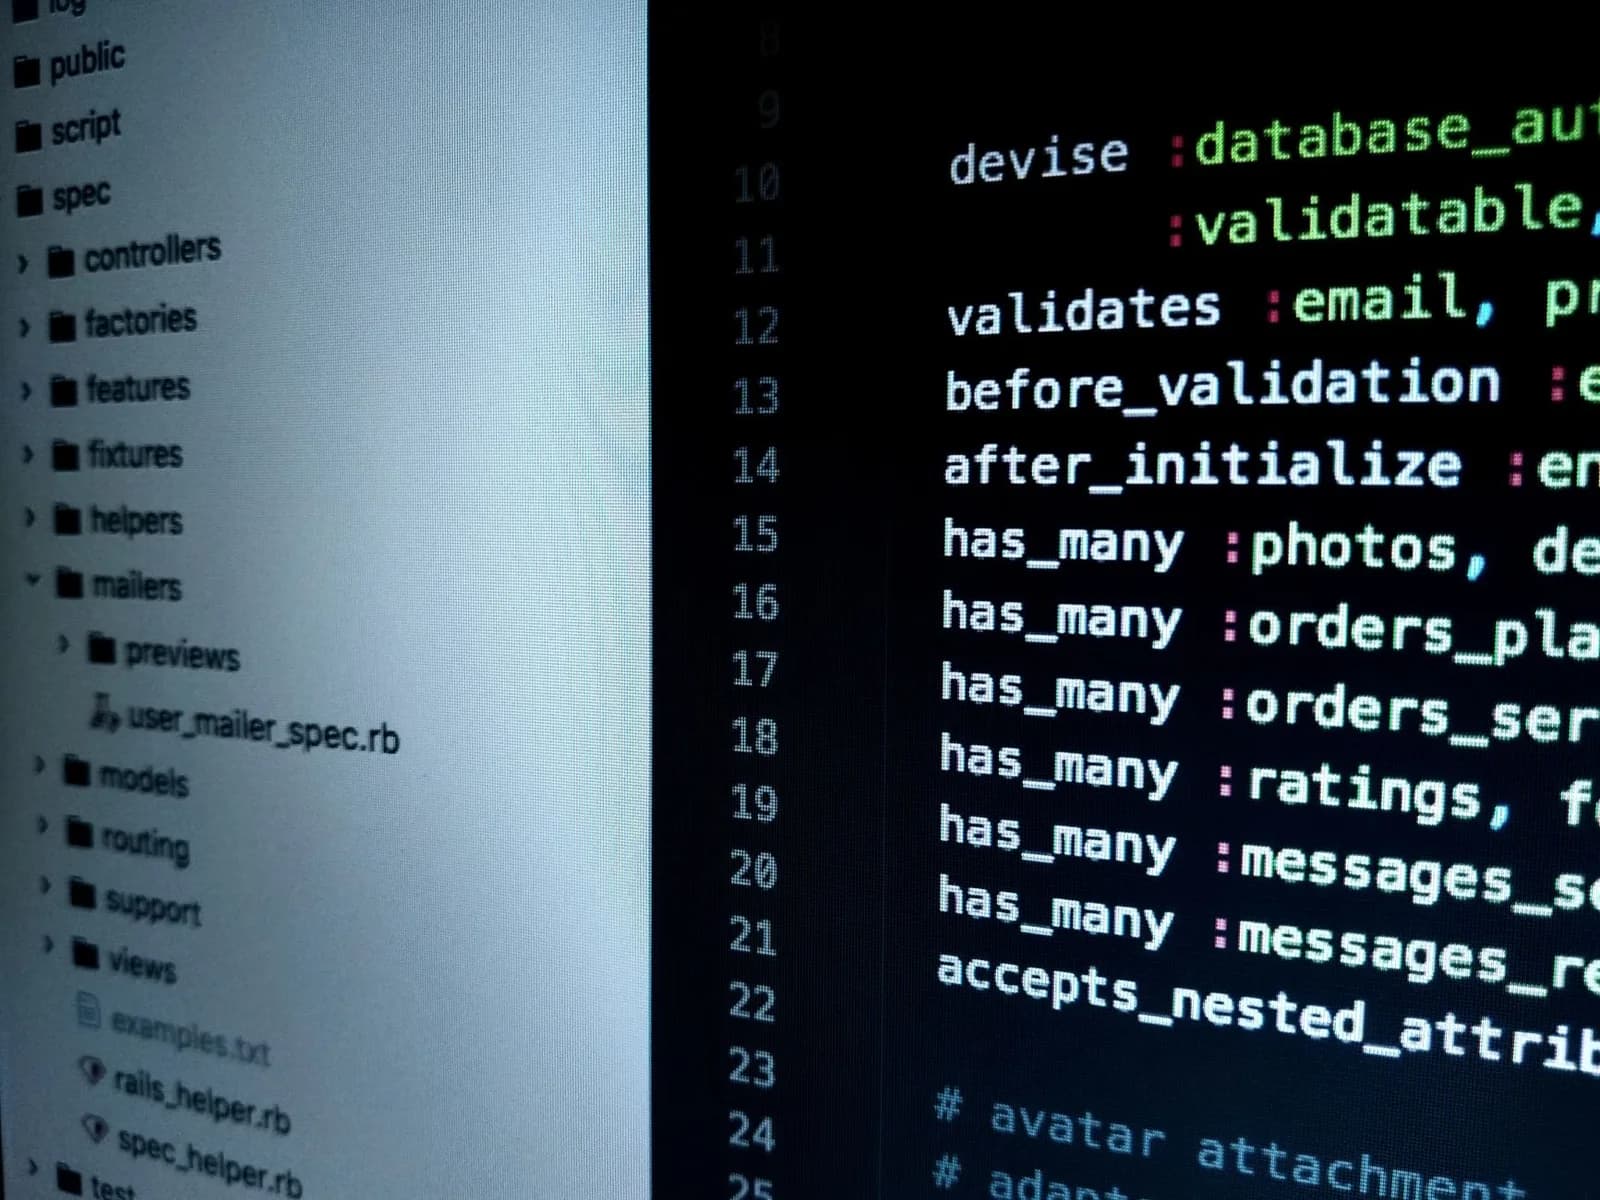
Attackers Backdoored Injective SDK on npm to Steal Crypto Wallet Keys
A compromised Injective Labs SDK package on npm was used to harvest private keys and seed phrases, security researchers reported.

AfroEuropa Newsroom
AfroEuropa desk
A software supply-chain attack targeting the developer tools of blockchain project Injective has renewed concern over the security of open-source package ecosystems that underpin much of the crypto industry, including projects and teams active across Europe.
According to reporting from BleepingComputer and Cointelegraph, attackers gained access to the GitHub repository behind the Injective Labs software development kit (SDK) and used that access to publish a malicious version of the package on the Node Package Manager, commonly known as npm. The tampered package was designed to steal cryptocurrency wallet private keys and mnemonic seed phrases from affected environments.
Keep reading
Italy's Exein Raises $270 Million for Physical AI Security, Hits $1.7B Valuation
Rome-based Exein has closed a $270 million round at a $1.7 billion valuation, described by its backers as making it Europe's most valuable cybersecurity startup.
Other highlights

Crypto Stocks Fall After Senate Declines to Advance Clarity Act
Shares of Coinbase, Circle and Galaxy dropped after the U.S. Senate failed to move forward a crypto market structure bill.
Follow the story
One newsletter, two continents
The Bridge brings you the tech, startups, and leaders moving between Africa and Europe in one sharp email each morning. No spam, unsubscribe anytime.